
Browser Fingerprinting Explained: Why It Still Matters for Privacy
October 29, 2026
•

10 min read
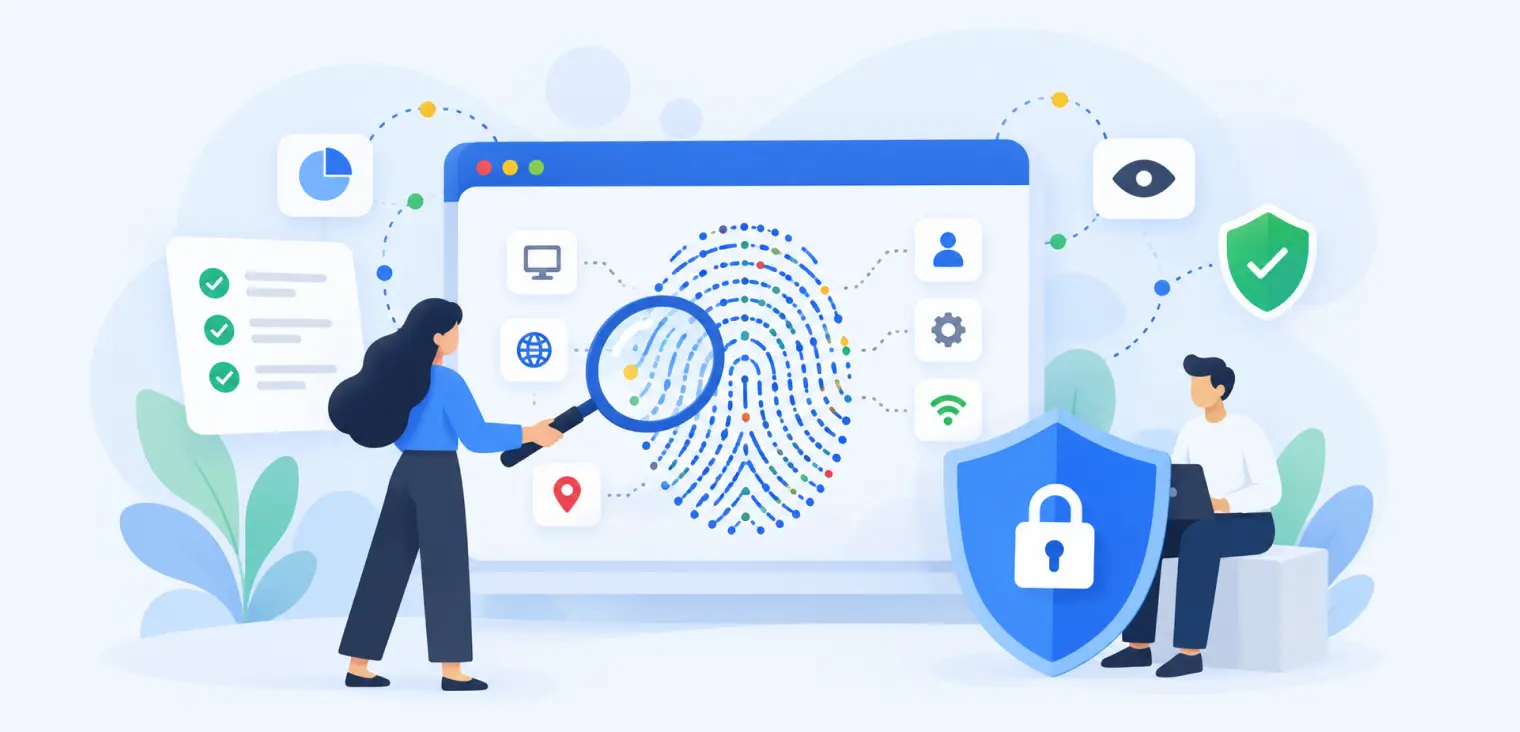
Table of contents
back
to the top
Browser Fingerprinting Explained: Why It Still Matters for Privacy
Most website owners know what cookies are. Fewer know that a browser can sometimes be recognised without storing a cookie at all.
That is the idea behind browser fingerprinting. Instead of relying on one identifier saved in the browser, a website or third-party script can collect characteristics of a visitor's browser and device, combine them, and use the result to distinguish that browser from others.
Fingerprinting has legitimate uses, including fraud detection and account security. But it can also be used for tracking and profiling in ways that are difficult for visitors to notice or control. For website owners, this creates an important question: if you have a cookie banner, are you also managing tracking that does not use cookies?
This guide explains how browser fingerprinting works, why it matters for privacy, and what businesses should review before adding analytics, advertising, security, or other third-party scripts.
What Is Browser Fingerprinting?
Browser fingerprinting is a way of distinguishing a browser by combining information about its configuration and behaviour.
A single detail, such as a visitor's preferred language, is unlikely to identify them. But language combined with screen size, time zone, browser version, graphics capabilities, fonts, and other signals may produce a much more distinctive pattern.
Imagine two people arriving at the same website. Both use the same browser. One has a different operating system, screen resolution, language setting, and collection of fonts. A fingerprinting script may use those differences to distinguish their browsers, even when neither has accepted an advertising cookie.
A fingerprint is not necessarily a person's real identity, and it is not always unique or stable. Browsers update, settings change, devices can look similar, and privacy protections can interfere with fingerprinting. Nevertheless, fingerprinting can sometimes help recognise a returning browser or link activity across visits.
The Mozilla Developer Network's explanation of fingerprinting describes the practice as combining distinguishing browser and system characteristics to identify a browser.
How Does Browser Fingerprinting Work?
Some fingerprinting techniques use information available through ordinary browser requests. Others run JavaScript to collect more details. Signals can include:
- Browser and operating system information.
- Screen dimensions, pixel ratio, and display settings.
- Preferred language and time zone.
- Available fonts and media capabilities.
- Graphics or audio processing characteristics.
- Browser settings and supported features.
- Network information, potentially including IP addresses.
A script may combine several signals into an identifier or a score that estimates whether two visits came from the same browser. The process can happen in the background while the visitor is reading a page.
Two terms are worth knowing. Passive fingerprinting uses information exposed through normal communication, such as request headers. Active fingerprinting makes additional checks, often through browser APIs, to observe particular characteristics.
What are canvas and WebGL fingerprinting?
Canvas fingerprinting asks the browser to draw something, such as text or a shape, and examines differences in the rendered result. Graphics hardware, fonts, operating systems, and software can influence that result.
WebGL fingerprinting examines characteristics of the browser's graphics capabilities or rendering. Audio-based techniques can similarly look for differences in how devices process sound.
These methods do not guarantee that a visitor will be uniquely identified. Their privacy concern is that small technical differences can become useful tracking signals when combined with others.
Browser Fingerprinting vs Cookies: What Is the Difference?
Cookies and browser fingerprinting can serve overlapping purposes, but they work differently.
| | Cookies | Browser fingerprinting | |---|---|---| | How identification works | A website stores or reads information associated with the browser | A script or service combines browser and device characteristics | | Does it require a cookie? | Yes, for cookie-based tracking | No | | Can visitors delete an identifier? | Cookies can normally be cleared | There may be no single stored identifier to delete | | Can it change over time? | Yes, if cookies expire or are cleared | Yes, as settings, software, or devices change | | Typical uses | Logins, preferences, analytics, advertising | Security, fraud prevention, recognition, profiling |
The biggest difference is user control. People are familiar with clearing cookies or declining marketing cookies. Fingerprinting can be harder to see because it may not create a visible browser-storage entry.
That does not make fingerprints permanent or foolproof. It means traditional cookie controls do not necessarily capture the full tracking picture.
Why Browser Fingerprinting Is a Privacy Concern
Fingerprinting becomes particularly sensitive when it is used to follow someone's activity rather than to provide a clearly explained service.
A third-party service could potentially recognise a browser on multiple sites that use its technology. A website could combine a fingerprint with an account, purchase, form submission, or other identifier. Over time, those connections may reveal browsing interests or patterns.
The concern is not only what the website knows during one visit. It is whether observations can be linked across sessions, purposes, or services without meaningful transparency or choice.
Fingerprinting can also create a false sense of anonymity. A visitor may delete cookies or use private browsing and assume they cannot be recognised. Those measures can reduce some forms of tracking, but they do not necessarily prevent every fingerprinting technique.
For marketers, the important principle is simple: a technology does not become privacy-friendly merely because it avoids cookies.
Is Browser Fingerprinting Illegal Under GDPR?
Not automatically. The legal assessment depends on the technique, its purpose, what information is accessed, and how that information is used.
In the EU, the ePrivacy rules can apply when technology stores information on, or accesses information from, someone's device. The European Data Protection Board has clarified the technical scope of these rules in its guidelines on Article 5(3) of the ePrivacy Directive.
In the UK, the Information Commissioner's Office explicitly includes device fingerprinting in its guidance on storage and access technologies. The ICO says the relevant PECR rules apply where fingerprinting involves storing information on, or accessing information stored on, a device.
Where the resulting information is personal data, GDPR or UK GDPR obligations may also apply. A fingerprint does not need to contain someone's name to raise personal-data questions if it can distinguish or be linked to an identifiable person.
For non-exempt fingerprinting, consent may be required before the relevant access takes place. Some strictly necessary or other qualifying uses may fall under an exception, but this needs a genuine purpose-based assessment. Advertising fingerprinting and security-related fingerprinting should not simply be treated as equivalent.
What About Fraud Prevention and Website Security?
Not every use of fingerprinting is intended to follow users around the internet.
A bank, ecommerce store, or account platform might analyse device characteristics to identify suspicious sign-ins, automated abuse, or unusual payment activity. In that context, fingerprinting may help protect customers and the service.
But using fingerprinting for security does not automatically remove all privacy obligations. The business still needs to understand which device information is accessed, whether an exception applies, how data is processed, who receives it, and how long it is retained.
An important practical question is whether the security provider reuses information for unrelated purposes. Technology deployed for account protection should not quietly become a tool for advertising profiling.
The right approach is to document the use case instead of assuming that every fingerprinting script is either prohibited or harmless.
Can Cookie Banners Stop Fingerprinting?
A properly configured consent management system can help control third-party scripts that use fingerprinting. But a cookie banner alone does not automatically detect or block every fingerprinting technique.
A banner is the user-facing part of the process. Behind it, website owners must determine which scripts run, what device information they access, what each tool does, and when it is allowed to load.
CookiePal's consent management platform offers consent banners, cookie scanning, categorisation, auto-blocking, and consent records. These are useful foundations for managing non-essential tracking scripts. However, fingerprinting requires a broader technical review: a traditional cookie scan cannot prove that all browser-fingerprinting behaviour has been discovered or prevented.
If your marketing, analytics, or security vendor uses fingerprinting, review that provider's documentation and test the implementation rather than relying only on a banner's appearance.
How Can Website Owners Check for Fingerprinting?
Start with an inventory of the scripts and services running on your website. Include your main pages, campaign landing pages, checkout, account areas, and embedded tools.
A CookiePal website compliance scan is a useful first step for identifying cookies and trackers. Then expand the review beyond cookies:
- List your vendors. Include analytics, advertising, fraud-prevention, chatbot, session-replay, and personalisation tools.
- Read their documentation. Look for browser fingerprinting, device identification, canvas, WebGL, device intelligence, and similar terms.
- Check script behaviour. Use browser developer tools and, where necessary, specialist testing to inspect network requests and browser API access.
- Test before consent. Find out which scripts load before visitors choose whether to accept optional tracking.
- Test rejection and withdrawal. Make sure non-exempt tracking responds correctly when consent is denied or later withdrawn.
- Document each purpose. Record whether the technology supports security, analytics, advertising, or another function, along with the applicable consent or exception decision.
Technical testing can be complex, and some fingerprinting is difficult to distinguish from ordinary browser functionality. Ask the developer or vendor for evidence when the behaviour is unclear.
Make Your Privacy Information More Accurate
A cookie policy that lists only cookie names may miss other technologies used by the website. Visitors should be told about relevant tracking practices in language they can understand.
For example, instead of saying only "we use cookies to improve our services," a business using device signals for fraud prevention might explain that it checks certain browser and device characteristics to detect suspicious activity.
If a vendor uses those characteristics for advertising or user profiling, the explanation should reflect that different purpose. Avoid vague phrases such as "anonymous technology" when browser activity can still be linked or recognised.
CookiePal's cookie policy generator and privacy policy generator can help structure website disclosures. Review the final wording against your actual technologies, including non-cookie tracking, and have it checked where appropriate.
Why Fingerprinting Still Matters Beyond Third-Party Cookies
Browser privacy protections continue to evolve. Some browsers limit cross-site tracking, reduce the amount of identifying information exposed, or introduce anti-fingerprinting measures. The W3C's fingerprinting guidance explains why seemingly harmless browser features can create privacy risks when combined.
These protections are valuable, but they do not make website tracking a solved problem. Businesses can still use scripts, device signals, first-party identifiers, and server-side systems in ways that require privacy review.
For website owners, the lesson is not to abandon analytics or useful security tools. It is to examine what each tool actually does instead of judging privacy by whether a familiar cookie name appears in the browser.
Build a Consent Process That Looks Beyond Cookies
The strongest privacy setup starts with visibility. Know which technologies run on your website, why they run, which providers receive information, and whether users have a meaningful choice.
Use a CookiePal compliance scan to begin reviewing cookies and trackers, then investigate any vendors that use device recognition or fingerprinting. Connect the results to your consent configuration, privacy disclosures, and ongoing script-review process.
Browser fingerprinting still matters because privacy is about what websites can learn and link about people, not simply what they store in a cookie. A well-designed cookie banner is useful. Understanding the tracking behind it is what makes the privacy process credible.
This article provides general information, not legal advice. Requirements depend on the technology, purpose, location of users, and applicable law.
Explore further
Link Decoration and Tracking Parameters: The Privacy Issue Marketers Miss
Click IDs and UTM parameters can carry identifiers through URLs, forms and servers. Learn when link decoration needs consent, how URL passthrough fits and how to audit it.
October 29, 2026
9 min
Do A/B Testing Tools Require Cookie Consent?
A/B tests can store IDs, share events and feed ad audiences. Learn when experiments need consent, when a narrow exemption may apply and how to run tests without ignoring privacy.
October 22, 2026
9 min
Cookies, Local Storage and Session Storage: What Is the Difference?
Cookies, local storage and session storage behave differently, but none is exempt from consent. Learn how each one works, which to use and how to review them in your consent process.
October 22, 2026
9 min