

GDPR and Data Storage: What’s the Right Retention Period
October 24, 2025
•

4 min read
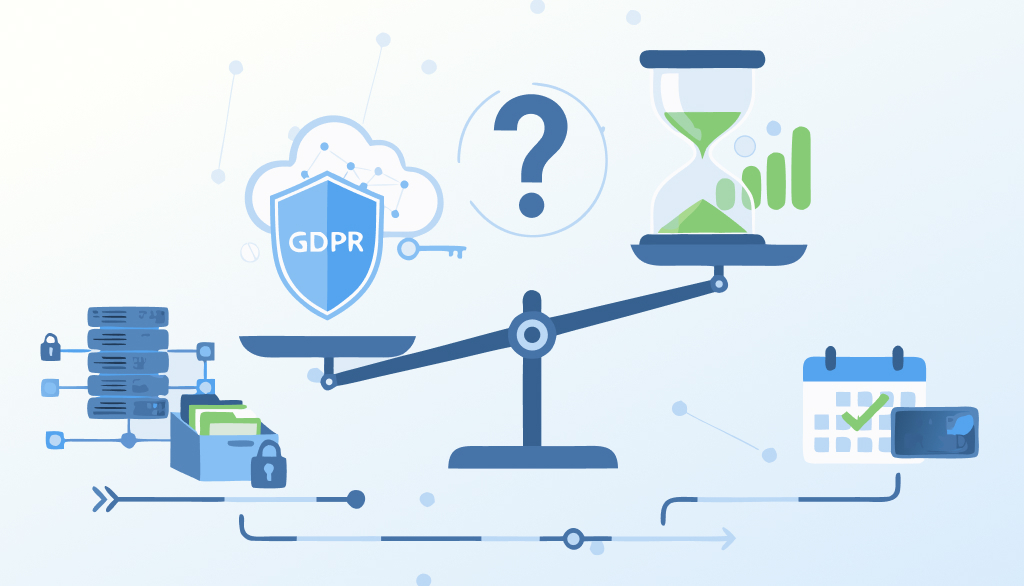
Table of contents
back
to the top
GDPR and Data Storage: What's the Right Retention Period?
When it comes to personal data, more isn't always better. Under the General Data Protection Regulation (GDPR), holding onto personal data longer than necessary can put your business at risk of non-compliance.
What Is Data Retention Under GDPR?
Data retention refers to the period of time a company stores personal data before it's deleted, anonymized, or archived. GDPR follows a purpose-based approach, meaning you can only keep personal data:
- For as long as it's necessary to fulfill the purpose it was collected for.
- No longer than needed, even if it's stored securely.
- If the reason you collected the data is no longer valid, you must delete or anonymize it.
Is There a GDPR Data Retention Limit?
The GDPR requires that:
"Personal data shall be kept in a form which permits identification of data subjects for no longer than is necessary." — Article 5(1)(e), GDPR
How to Set GDPR-Compliant Retention Periods
Organizations should build a Data Retention Policy that outlines:
- Why data is collected
- How long it is kept
- When and how it is reviewed or deleted
- Processes for deletion or anonymization
- Who is responsible for enforcement
Your Record of Processing Activities (ROPA) should reflect retention timelines.
Risks of Keeping Data Too Long
- Security risk: More data means larger breach impact.
- Regulatory risk: Non-compliance with GDPR principles.
- Fines: Up to €20 million or 4% of global turnover.
Retention and User Consent
If relying on user consent:
- Set a clear expiration period (e.g. 12–24 months).
- Renew consent to continue processing after that.
- Delete or anonymize data if consent is withdrawn or expired.
CMPs (Consent Management Platforms) help enforce time-bound consent tracking.
Final Takeaway
To stay GDPR compliant:
- Only keep data as long as needed.
- Document your justification for retention periods.
- Regularly audit and purge outdated records.
A clear data retention policy is essential for privacy compliance, trust, and risk reduction.
Sources
Explore further
Browser Fingerprinting Explained: Why It Still Matters for Privacy
Fingerprinting can recognise a browser without storing a cookie, so your banner may not cover it. Learn how it works, when consent applies and how to audit your scripts.
October 29, 2026
10 min
Link Decoration and Tracking Parameters: The Privacy Issue Marketers Miss
Click IDs and UTM parameters can carry identifiers through URLs, forms and servers. Learn when link decoration needs consent, how URL passthrough fits and how to audit it.
October 29, 2026
9 min
Do A/B Testing Tools Require Cookie Consent?
A/B tests can store IDs, share events and feed ad audiences. Learn when experiments need consent, when a narrow exemption may apply and how to run tests without ignoring privacy.
October 22, 2026
9 min